

A suspicious email lands in your inbox — or worse, a client calls saying they got a strange email from you. Before you can respond, you need to answer one question: was your email account actually broken into, or did someone just fake your address? The answer changes everything about how you respond.
These are two completely different attacks with different causes, different risks, and different fixes. This guide explains each one clearly, shows you how to diagnose which one happened using free tools, and tells you exactly what to look for in email headers — including how to find DMARC failures and unauthorized sending IPs.
Understanding email impersonation is the first step toward protecting your business. Across the USA, small and mid-sized businesses are increasingly targeted by attackers who exploit the confusion between these attack types to steal money, data, and trust.
The Three Types of Email Impersonation
When someone receives a fraudulent email that appears to come from a person or business they trust, one of three things happens, and each form of email impersonation requires a different response, a different fix, and leaves a different trail in the email headers.
1. What Is Email Account Compromise (Business Email Compromise / BEC)?
DEFINITION
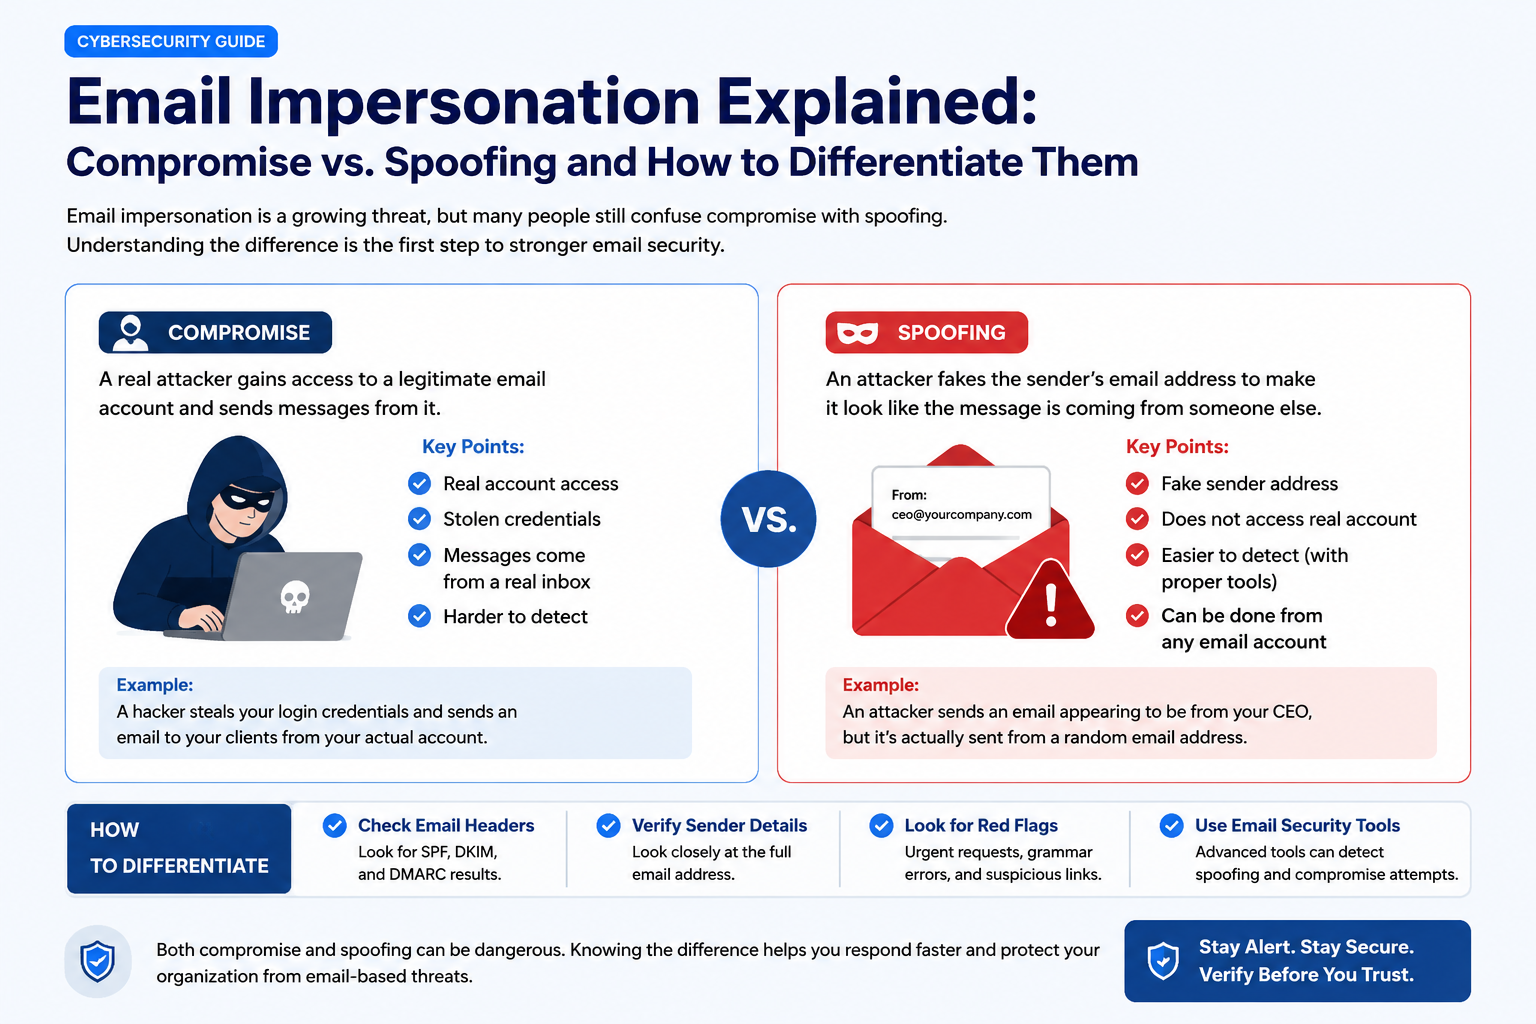
Account compromise means an attacker has gained actual access to a legitimate email account — through stolen credentials, phishing, or brute force — and is sending emails from inside it using the real account on the real mail server.
This is the most dangerous type because the email is technically legitimate. It passes every authentication check. It comes from the real server. The reply-to address is real. If you reply, the attacker sees it.
How it happens: The victim clicks a phishing link and enters their password, reuses a password that was leaked in a data breach, or uses a weak password that gets brute-forced. Multi-factor authentication (MFA) prevents most account compromise attacks.
Signs of account compromise:
- The email passes SPF, DKIM, and DMARC checks
- The sending IP belongs to the legitimate mail provider (Google, Microsoft, etc.)
- The victim has login activity from unusual locations or times
- Sent mail folder shows emails the account owner never sent
- Inbox rules have been created to delete or forward messages
2. What Is Email Spoofing (Domain Spoofing)?
DEFINITION
Domain spoofing means an attacker is forging the From address to show a legitimate domain (e.g., [email protected]) without having any access to that domain or its email accounts. The email is sent from an external server the attacker controls.
This is the attack that DMARC, SPF, and DKIM are specifically designed to prevent. If a domain has a DMARC policy of p=reject, spoofed emails are blocked before delivery. If the policy is p=none — which is the case for the majority of small business domains — spoofed emails are delivered as normal.
How it happens: The attacker simply sets the From field in their email client to any address they want. Without authentication enforcement, nothing stops them. They don’t need access to anything.
CRITICAL POINT
Domain spoofing does not require the attacker to compromise anything. They need zero access to your systems, your domain, or your email provider. They just need your domain name — which is public information.
3. Display Name Spoofing
DEFINITION
Display name spoofing means an attacker sets the visible sender name to match a trusted person (e.g., “Sarah Johnson — CEO”) but uses a completely different, attacker-controlled email address. The actual sending domain is different from the displayed name.
This is the lowest-effort attack and the hardest to defend against technically, because there is nothing technically wrong with the email. The From address is real and authenticated — it just belongs to the attacker, not to the person being impersonated.
Most email clients show only the display name by default and hide the actual address. A recipient who doesn’t click to expand the sender details may never see that the address is [email protected] rather than [email protected].
DMARC cannot prevent display name spoofing because the sending domain is not being forged — it’s a different domain entirely, sent legitimately.
Intro: “Use this table to quickly identify which form of email impersonation you are dealing with based on the technical evidence available in the email headers.”
<<<In the middle, below ‘Side-by-Side, and before the table’>>>

How to Read Email Headers to Diagnose What Happened
Email headers contain the full technical trail of an email — every server it touched, every authentication check it passed or failed, and the actual IP address it was sent from. Most people never see them. When something suspicious happens, they’re the first place to look.
FREE TOOL
Use the Microsoft Message Header Analyzer (MHA) at mha.azurewebsites.net — it’s free, requires no login, and parses raw email headers into a readable format in seconds.
>>>[ INFOGRAPHIC: How to Read Email Headers to Detect Spoofing — embed blog-infographic.html here ]>>>
Step 1 — Get the Raw Email Headers
- Gmail
Open the email → click the three-dot menu (⋮) in the top right of the message → select “Show original” → copy all the text in the box.
- Outlook (Desktop)
Open the email → go to File → Properties → copy the text in the “Internet headers” box at the bottom.
- Outlook (Web)
Open the email → click the three-dot menu → select “View → View message source” or “View message details”.
- Paste into MHA
Go to mha.azurewebsites.net → paste the header text into the box → click “Analyze headers”.
Step 2 — Find the Authentication Results
In the MHA output, look for the section labeled Authentication-Results. This is the most important section. Here’s what a spoofed email looks like versus a legitimate one.

Step 3 — Find the Sending IP Address
In MHA, look for the Received headers — specifically the first one (the originating server). It will contain the actual IP address the email was sent from. This is what you use to determine whether the sender was legitimate.

If the IP address in the Received header does not belong to the legitimate email provider (Google Workspace IPs start with 209.85. or 74.125., Microsoft 365 IPs are in the 40.x and 52.x ranges), the email was not sent from the legitimate account.
Step 4 — Understand the DMARC Failure Reason
When DMARC fails, MHA will show a reason code. Here’s what each one means:
KEY INSIGHT
If you see dmarc=fail (p=NONE), it means the email was spoofed AND it was delivered successfully because the domain had no enforcement policy. This is the most common finding in small business email fraud investigations.
Quick Diagnosis Guide
Use this decision tree to quickly determine what type of attack occurred:
1. Does the sending IP belong to the legitimate mail provider?
Yes: Likely account compromise or legitimate email. Check login history.
No: Domain spoofing. The account was not accessed.
2. Does the Authentication-Results show SPF pass or fail?
SPF pass + DMARC pass: Sent from authorized server. Account compromise or legitimate.
SPF fail + DMARC fail: Domain spoofing confirmed. Sending IP is unauthorized.
3. Does the visible From name match the actual From address?
Name matches address: Not display name spoofing.
Name does not match address: Display name spoofing. The actual address is different from what was shown.
4. If account compromise — check for inbox rules and login history.
In Gmail: Settings > See all settings > Filters and Blocked Addresses, and check Last account activity.
In Outlook/M365: Admin center > Sign-in logs, and check mail flow rules.
What To Do If Email Is Compromised
If the email headers and login history confirm account compromise, every minute matters. Here is exactly what to do, in order:
- Change your password immediately using a device you trust and have not used to log into that account recently.
- Enable multi-factor authentication (MFA) if it is not already active. This is the single most effective step you can take.
- Check your inbox rules in Gmail or Outlook for any forwarding rules or filters the attacker may have created to redirect or delete emails.
- Review your sent folder for any emails sent by the attacker while they had access.
- Notify anyone who may have received fraudulent emails from your account so they can disregard requests for payments, credentials, or sensitive information.
- Contact your IT provider or a cybersecurity specialist. Businesses across the USA that experience account compromise often find attackers have been inside the account for days or weeks before detection.
- Run a full audit of connected third-party apps that have access to your account — revoke any that are unfamiliar.
IMPORTANT
Do not simply change your password and move on. Attackers frequently install inbox rules that persist after a password reset. You must audit rules, connected apps, and login history as part of your recovery.
What To Do If Your Email Is spoofed
If the investigation confirms domain spoofing, your account has not been breached, but your domain is being used to deceive others. Here is how to stop it:
- Run a SPF DKIM DMARC check on your domain immediately. Free tools like MXToolbox or our Email Trust Score scanner at emailtrustscore.threatalliance.com will show your current configuration and score in under 60 seconds.
- If your DMARC policy is set to p=none, upgrade it to p=quarantine first, then p=reject once you have confirmed all your legitimate sending sources are included in your SPF record.
- Audit your SPF record to make sure every legitimate sending source is listed. Missing tools like HubSpot, DocuSign, or Zoom are a common cause of SPF failures even for legitimate emails.
- Implement DKIM signing through your email provider. Google Workspace and Microsoft 365 both support DKIM and the setup takes less than 30 minutes.
- Add MTA-STS to enforce encrypted connections for inbound email, preventing attackers from intercepting email in transit.
- Notify your contacts that your domain may be used in spoofing attempts so they can be vigilant about verifying requests.
If you are a USA-based business dealing with active spoofing fraud involving financial transactions, report the incident to the FBI Internet Crime Complaint Center (IC3) at ic3.gov.
KEY POINT
Spoofing cannot be stopped at the recipient level. The fix must happen on your domain. Until your DMARC policy is set to p=reject and your SPF and DKIM records are correctly configured, anyone in the world can send email pretending to be you.
How to Protect Your Domain from Spoofing
If the investigation reveals domain spoofing — the most common finding — the fix is implementing proper email authentication on your domain. This involves three records:
SPF (Sender Policy Framework): A DNS record that lists every server authorized to send email as your domain. If a server not on this list tries to send as you, SPF fails. The most common problem: SPF records become outdated as new tools (HubSpot, DocuSign, Zoom) are added without updating the record.
DKIM (DomainKeys Identified Mail): A cryptographic signature added to every outgoing email. The recipient’s server verifies the signature against a public key published in your DNS. If the email was modified in transit or sent from an unauthorized server, DKIM fails.
DMARC (Domain-based Message Authentication, Reporting and Conformance): The enforcement layer that tells receiving servers what to do when SPF or DKIM fails. p=none means do nothing. p=quarantine means send to spam. p=reject means block entirely. Most businesses are stuck at p=none — which means their domain can be spoofed freely.
MTA-STS (Mail Transfer Agent Strict Transport Security): Enforces encrypted connections for inbound email, preventing downgrade attacks and interception of email in transit.
Running a SPF DKIM DMARC check on your domain takes under a minute and will tell you exactly where your gaps are. For USA businesses, leaving these records unconfigured is one of the most common and most preventable causes of email fraud losses.
Find out if your domain can be spoofed right now
Our free Email Trust Score scanner checks your SPF, DKIM, DMARC, and MTA-STS configuration and gives you a score out of 10 — in under 60 seconds.
Summary
The key distinction to remember: account compromise means the attacker is inside the account. Domain spoofing means the attacker is pretending to be the account from outside. The email headers — specifically the sending IP address and the Authentication-Results section — tell you definitively which one occurred.
For domain spoofing, the fix is enforcing DMARC at p=reject. For account compromise, the fix is MFA, password reset, and auditing inbox rules. For display name spoofing, the fix is user education combined with email security awareness training.
Most small businesses are vulnerable to domain spoofing right now without knowing it. If you’ve never checked your domain’s DMARC policy, there is a reasonable chance anyone could be sending emails pretending to be you at this moment.
No matter which form of email impersonation you are dealing with, the right first step is always the same: get the evidence from the email headers, identify the attack type, and then take targeted action. If you are a USA business and are unsure where to start, Threat Alliance offers a free consultation to walk you through your exposure.
Frequently Asked Questions
1. What is email account compromise and how can I tell if it happened to my business?
Email account compromise usually involves unauthorized access to a real mailbox through stolen credentials or phishing attacks. We recommend reviewing login activity, sent emails, inbox rules, and authentication settings immediately to determine whether someone gained access to your account.
2. How often should my business run an SPF DKIM DMARC check?
We recommend checking your email authentication records whenever you add new email platforms, marketing tools, or communication services. Regular reviews help ensure legitimate emails are delivered properly while reducing the risk of unauthorized messages appearing to come from your domain.
3. Can attackers fake my company email address without hacking my account?
Yes. Attackers can forge a business email address without accessing the actual mailbox or internal systems. This commonly happens when domain protections are not fully configured, allowing fraudulent emails to appear legitimate to customers, vendors, employees, or partners.
4. How can I protect my business from email impersonation attacks?
We recommend implementing proper authentication records, enabling multi-factor authentication, training employees to recognize suspicious emails, and regularly reviewing domain security settings. Combining technical protections with employee awareness significantly reduces the likelihood of fraudulent emails reaching intended recipients.
5. What is email spoofing and why is it dangerous for small businesses?
Email spoofing allows attackers to send messages that appear to come from a trusted business or employee. These attacks can damage customer trust, trigger fraudulent payments, expose sensitive information, and create long-term reputational issues if not addressed quickly and properly.



 Threat Alliance 3075 W Ray Rd STE 200, Chandler, AZ 85226

 (480) 576-5833